





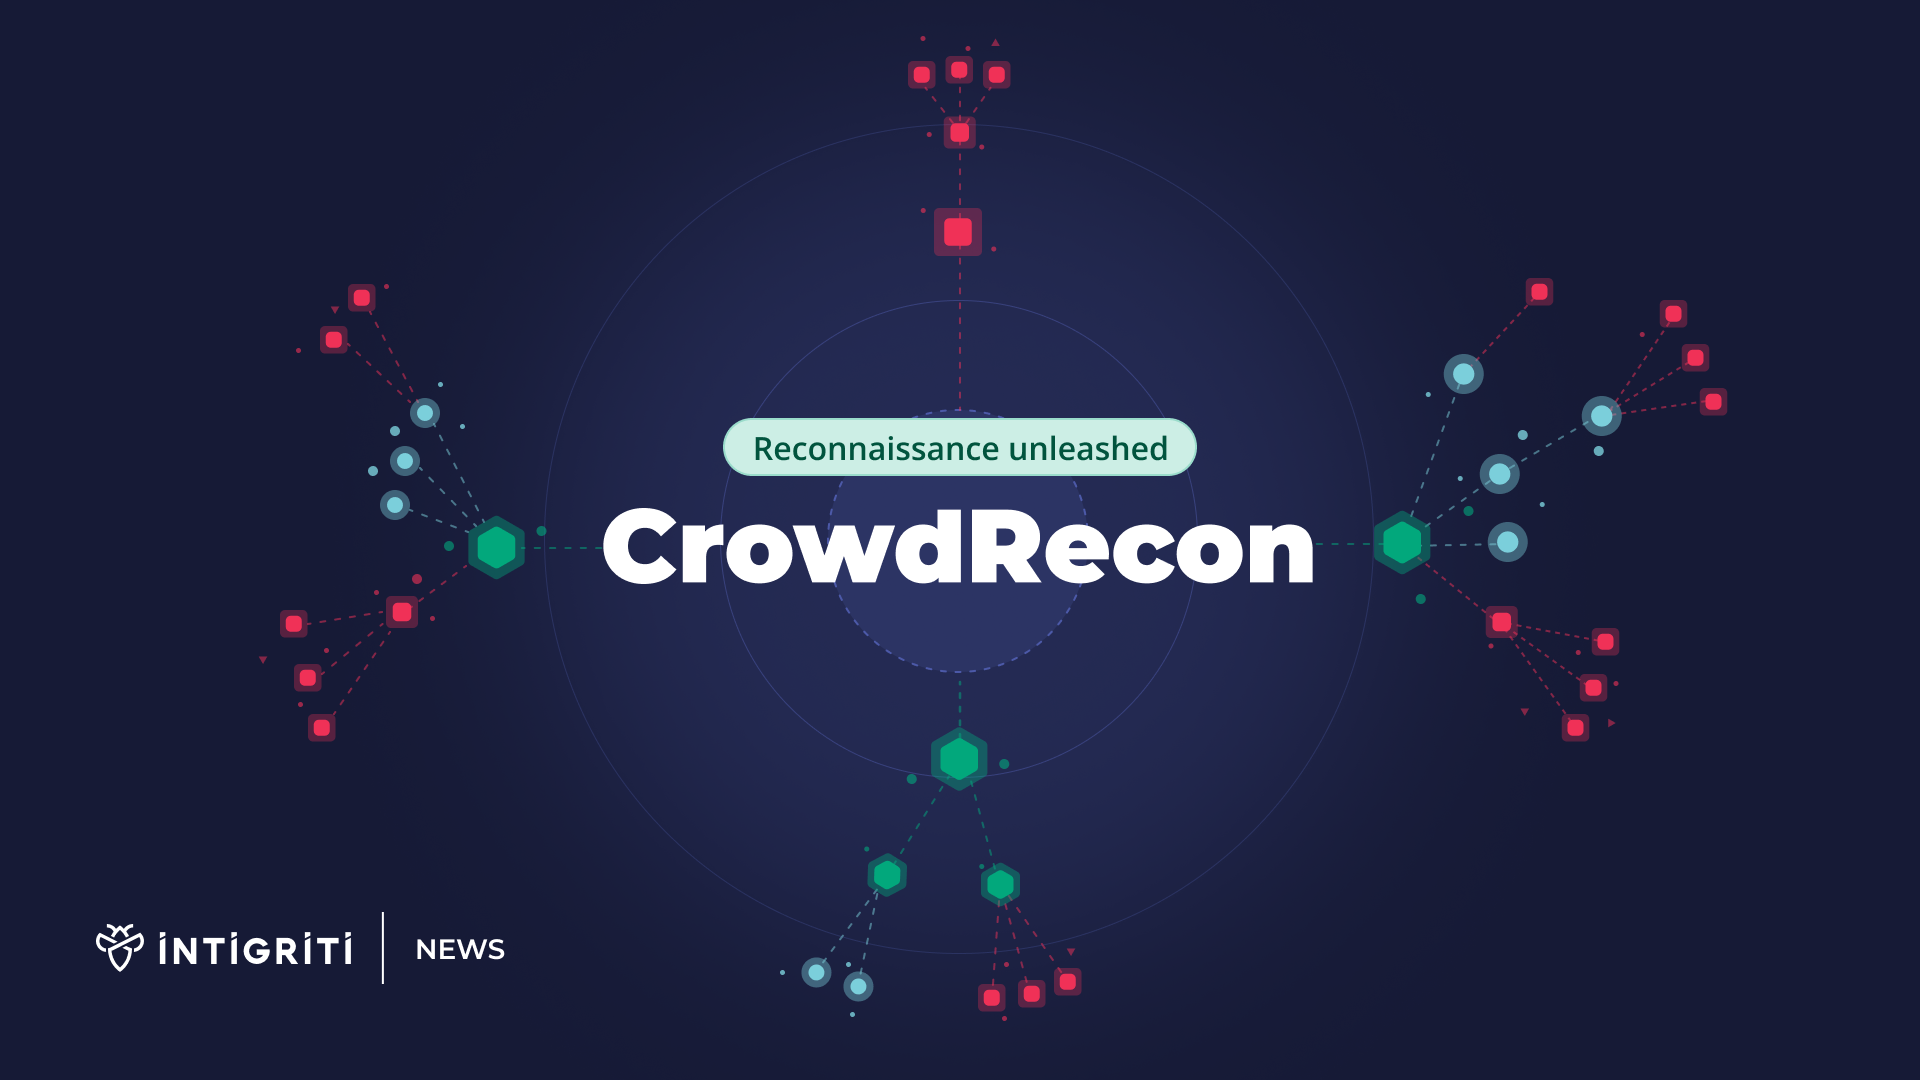
CrowdRecon
Before every report, there is recon. Turn that data into intelligence.
CrowdRecon turns real-world hacker reconnaissance into continuous, actionable insights. It helps security teams understand real researcher behavior across their attack surface, while giving researchers new ways to be recognized and rewarded beyond accepted vulnerability reports.


A new insights layer
Your attack surface changes faster than scope, scanners, and internal inventories can reflect. CrowdRecon adds a trusted hacker reconnaissance layer to the exposure inputs you already use, helping your team understand what researchers discover, explore, ignore, and return to before a final finding is submitted.
Your tools show what exists. Researchers show what deserves attention.
ASM, scanners, inventories, and internal dashboards all help map exposure. What often remains harder to see is how researchers engage with your attack surface in practice. That leaves teams still asking:

What are researchers finding that we are not?
Unexpected assets, forgotten subdomains, exposed environments, or paths already visible to trusted hackers.
Where is attention going?
Which areas are being explored, ignored, revisited, or treated as worth deeper investigation before a report exists?
What does silence mean?
A quiet program does not always mean there is nothing to find. It may mean that the scope needs to be expanded or clarified, or that certain areas are not getting enough coverage.
See what CrowdRecon reveals
CrowdRecon captures trusted hacker reconnaissance, validates what matters, and turns it into exposure insight your team can review, route, and act on before a vulnerability report exists.

Newly exposed assets
See which unknown, forgotten, or unexpectedly visible assets researchers uncover, to see what is actually discoverable beyond your own tools.

Scope and coverage signals
Understand where researchers explore, ignore, or return, so you can see whether your program reflects real engagement.

Vulnerability signals
Anticipate where the next vulnerability is likely to emerge based on trusted hacker recon signals, so your team can investigate and act before a report lands.
The process behind the signal
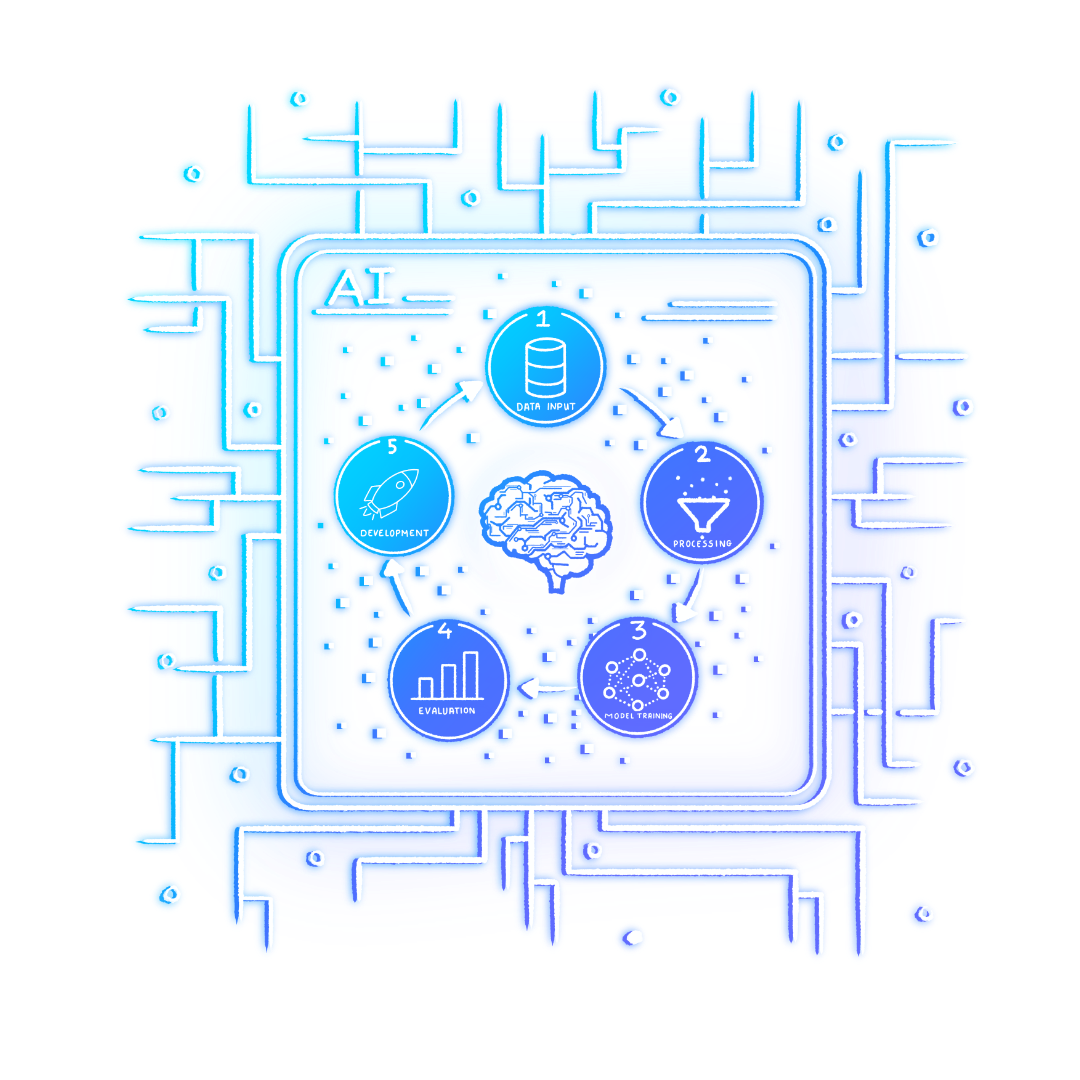
CrowdRecon creates a continuous loop between researchers activity and security action. As researchers explore, their recon signals are captured, validated, and turned into useful context for security teams. That feedback creates better visibility, stronger incentives, and more focused recon over time.
Capture
Hackers log useful recon activity as they explore assets, paths, endpoints, patterns, and context that may explain where attention is going.
Validate
Recon contributions are checked for quality, relevance, and usefulness, so teams are not working from raw noise or unverified volume.
Share
Validated recon becomes structured insight for security teams and useful context for hackers, showing what was explored and what may need follow-up.
Incentivize
Hackers are rewarded and recognized for high-quality recon, creating a stronger loop between participation, better context, and future opportunities.
New ways to reward the crowd
Choose the reward model that fits your program, from direct rewards for validated recon to leaderboard-based incentives to future bounty kickbacks.

Direct rewards for validated recon
Reward researchers when submitted recon is reviewed and accepted as useful, even if it does not become a vulnerability report.

Leaderboard and recognition
Recognize top contributors through company or global leaderboards, with points and potential rewards tied to high-quality recon activity.

Kickback from future vulnerabilities
If validated recon later contributes to an accepted vulnerability, the original recon contributor may receive a share of the bounty.
Frequently asked questions
CrowdRecon is currently in private beta. We’re preparing to open access more widely soon. If you’d like to be among the first to try it, join the waitlist below.
Attack Surface Management tools help you understand what is exposed. CrowdRecon helps you understand how trusted hackers engage with that exposure in practice. It works alongside your existing tools by turning researcher reconnaissance into structured insight your team can review before and between vulnerability reports.
Your program continues to work as it does today, with validated vulnerability reports as the primary proof point. CrowdRecon adds a layer of recon and exploration evidence between reports, helping your team see what trusted hackers are finding, exploring, ignoring, or returning to before a final finding is submitted. That context can support scope reviews, coverage decisions, and follow-up without changing how your core program runs.


Join the waitlist
Join CrowdRecon early: Get access to the private beta and see how recon becomes actionable signals for your security team.
CrowdRecon recognizes that the community not only finds vulnerabilities, but it also creates context, discovers hidden surfaces, shows where attention is forming, and helps customers understand how their external environment is interpreted by real researchers. This is an important step in how we think about the future of human-led exposure validation.


Radu Voloaga
Senior Product Manager

Related blog posts
Want a bit more context before the announcement? These posts are where the thread starts.


Reconnaissance for exposure management: why context matters in the AI era
Business Insights
June 29, 2026

The between-reports problem: why security teams miss what attackers see
Business Insights
July 20, 2026

Vulnerability disclosure for AI safeguards. How open should programs be and what incentives are necessary?
Business Insights
March 24, 2026

Common AI misconceptions debugged!
Business Insights
April 17, 2026

Vulnpocalypse Now? How AI is changing vulnerability discovery
Business Insights
April 23, 2026