
Bug Bytes #216 – SQL injections, Android XSS and Writing Quality Reports


Bug Bytes is a weekly newsletter curated by members of the bug bounty community. The second series is curated by InsiderPhD. Every week, she keeps us up to date with a comprehensive list of write-ups, tools, tutorials and resources.
This issue covers the week from October 23rd to October 29th
Intigriti News
From my notebook

HackTheBox – Gofer & Binary Analysis of notes [HackTheBox Gofer]
Thousands of remote IT workers discovered to be North Korean Spies
Let’s Hack Together! Follow Along Livestream w/ Gerald Auger, PhD

@Shenetworks: Leveraging Content Creation to Build a Career in Cybersecurity
They Hired Him to Snoop a Target, but Something Felt Very Wrong🎙Darknet Diaries Ep. 99: The Spy
Cloud Security Tools from Cloud Pentest Lab | DeRF |Stratus Red Team
EP149 Cloud Security: Shared Responsibility, Shared Fate, Shared Faith?
Cyber sloppiness, and why does Google really want to hide your IP address?
Risky Business #726 — Okta owned while Cisco takes a massive L
220 – Windows Kernel Bugs, Safari Integer Underflow, and CONSTIFY

Beginner
Simple Tips for Bug Bounty Beginners: Finding Open Redirect Bugs
Looking for Broken Access Control Vulnerabilities in websites
Mastering SQL Injection on DVWA Low Security with Burp Suite: A Comprehensive Guide — StackZero
A Guide to LFI Discovery: Uncover Vulnerabilities and Enhance Web Security | Bug bounty
Intermediate
Advanced

Security Research
Bugs
XSS on the Oauth callback URL with CSP bypass leading to zero-click account takeover
Beyond Error Messages: Super Admin Deletion due to Broken Access Control (€€€)
One Bug at a Time: Patent Pirating using IDOR | RE’ing US Patent and Trademark Office for fun
Securing Data: How I Quickly Accessed 3000 Student Records in under 5 Minutes
CTF challenges

Hakky54/certificate-ripper: 🔐 A CLI tool to extract server certificates
Arsenal – Just A Quick Inventory And Launcher For Hacking Programs
PostLeaks Tool that searches for sensitive data in public Postman API assets

You may also like

October 30, 2026
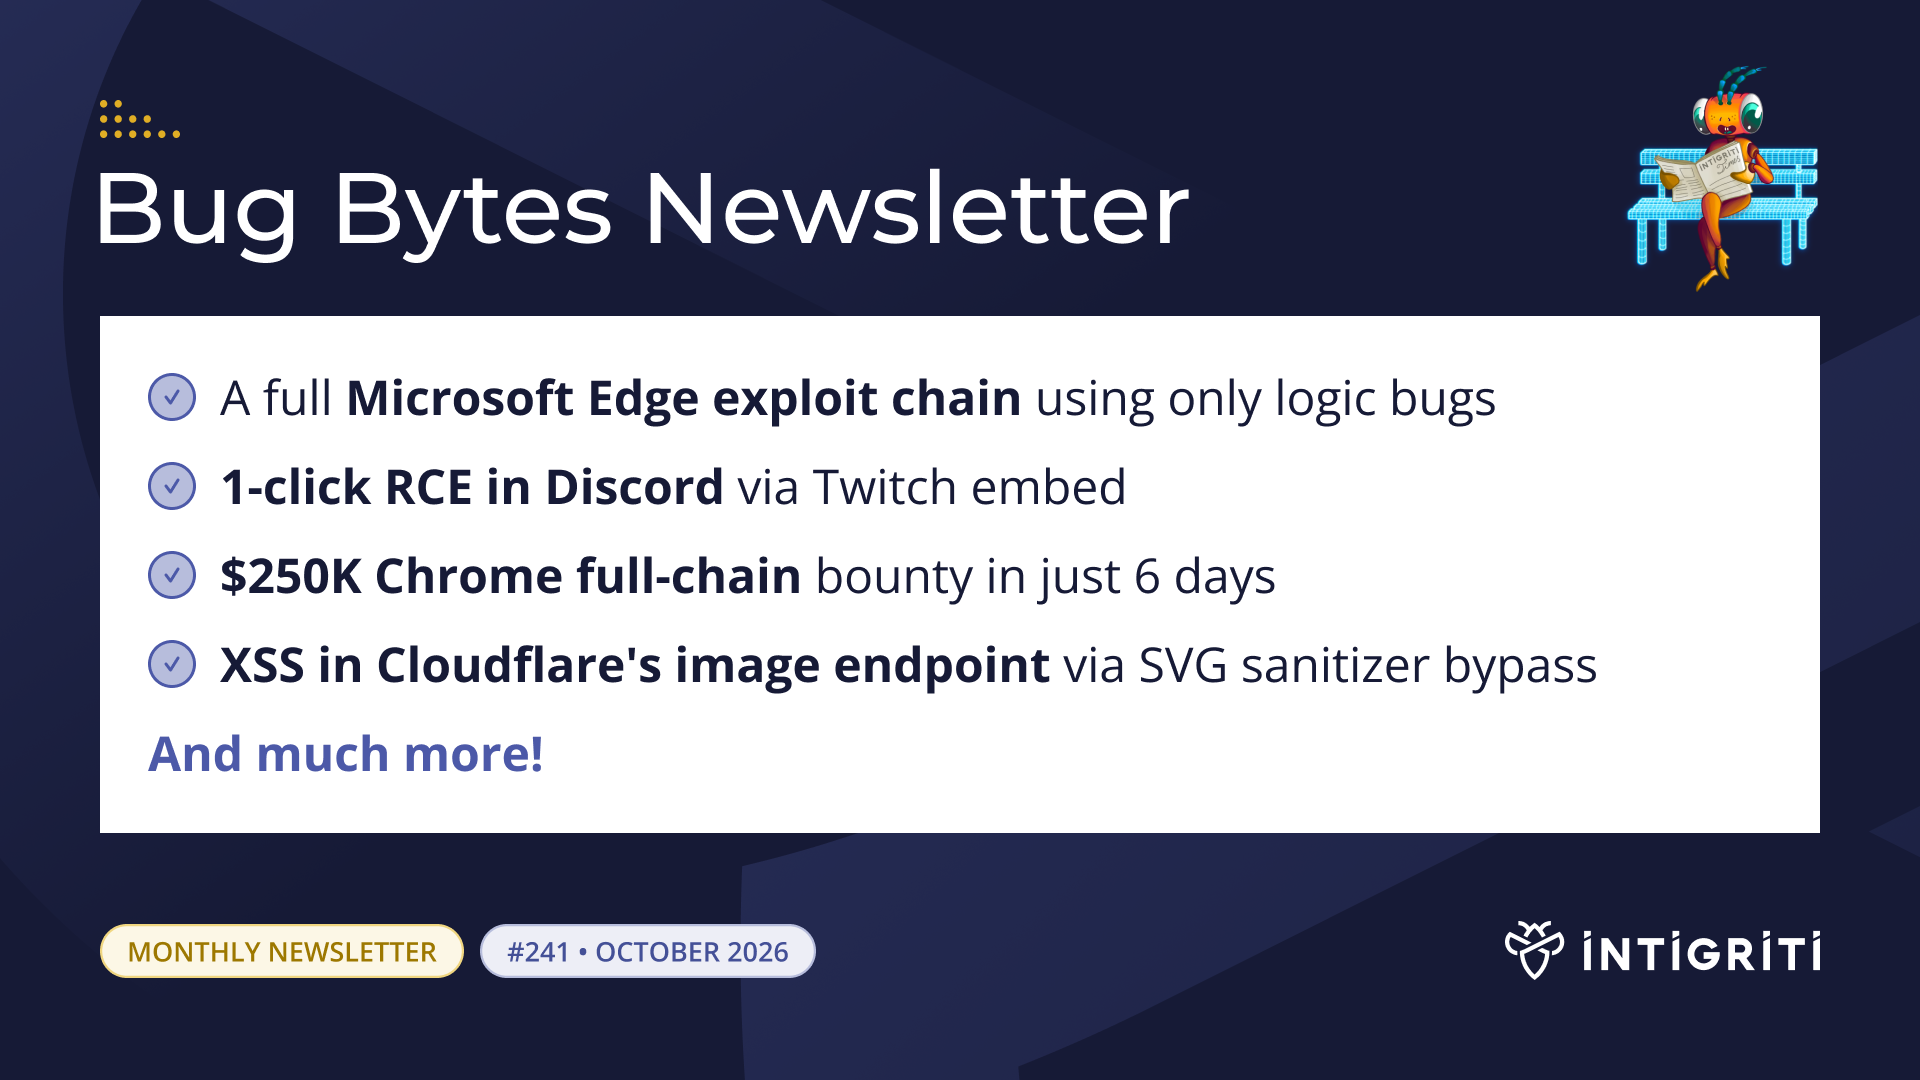
Intigriti Bug Bytes #241 - October 2026 🚀
Welcome to the latest edition of Bug Bytes! In this month's issue, we'll be featuring: A full Microsoft Edge exploit chain using only logic bugs 1-click RCE in Discord via Twitch embed $250K Chrome full-chain bounty in just 6 days XSS in Cloudflare's image endpoint via SVG sanitizer bypass $90K Goog
September 25, 2026
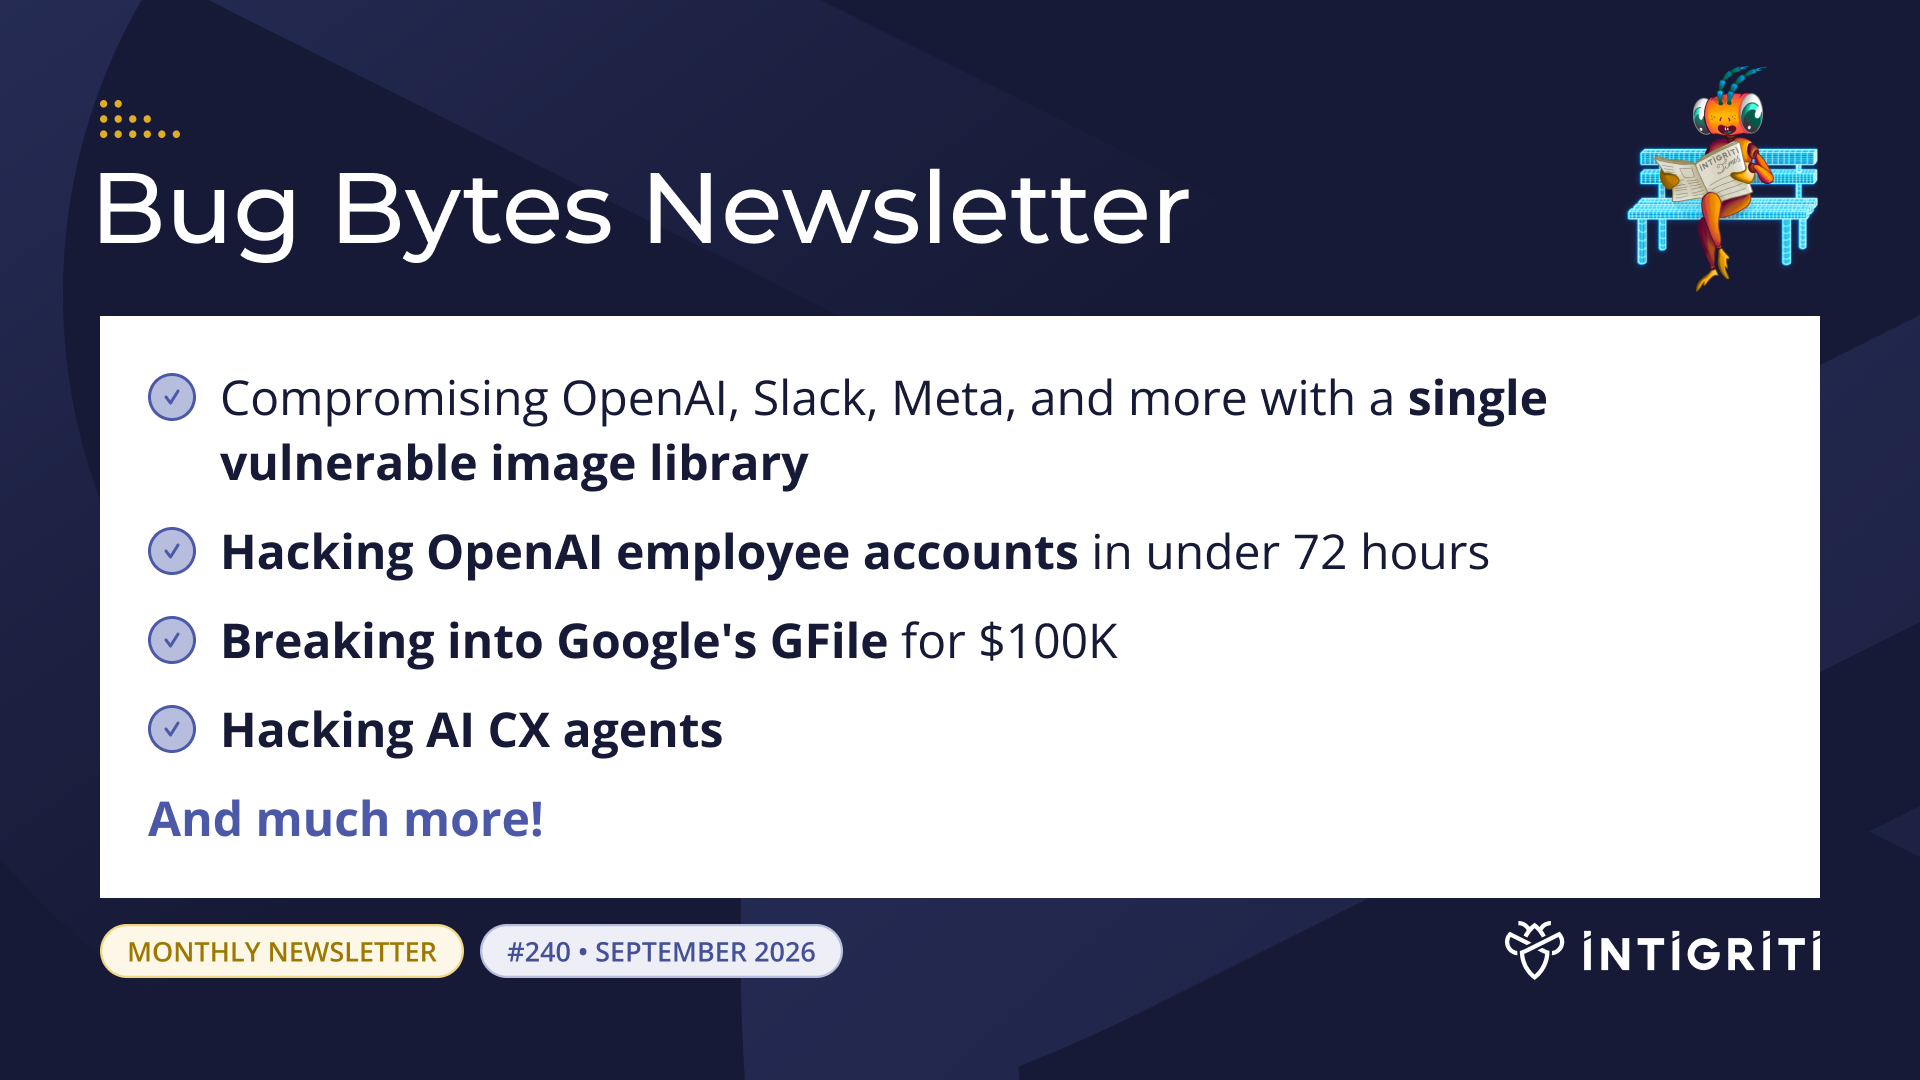
Intigriti Bug Bytes #240 - September 2026 🚀
Welcome to the latest edition of Bug Bytes! In this month's issue, we'll be featuring: Compromising OpenAI, Slack, Meta, and more via a vulnerable image library Hacking OpenAI employee accounts in under 72 hours Breaking into Google's GFile for $100K Hacking AI CX agents Turbo Intruder 2 surpassing

August 28, 2026
Intigriti Bug Bytes #239 - August 2026 🚀
Welcome to the latest edition of Bug Bytes! In this month's issue, we are featuring: Intigriti as the new provider for Adobe's Bug Bounty Program CSS injection as an attack vector inside your email inbox AI doing novel security research: the HTTP Terminator 169 offensive recon skills in one AI-ready