




Bug Bytes #195 – LastPass discovery, learning to code, and a complete guide to SSRF
By travisintigriti
March 8, 2023
Last updated on August 8, 2026
Bug Bytes is a weekly newsletter curated by members of the bug bounty community. The second series is curated by InsiderPhD. Every week, she keeps us up to date with a comprehensive list of write-ups, tools, tutorials and resources.
This issue covers the weeks from February 27th to March 5th
Intigriti News
From my notebook
LastPass says employee’s home computer was hacked and corporate vault taken
Web Cache Poisoning” which I utilized to deface/disable the target web application in the realtime
Other Amazing Things

Carving Exfiltrated Network Data from a Hack (Python & Scapy)
Announcing HTB Seasons | Open Beta – Hackers Wrath (Ippsec’s Thoughts on the New Hack The Box Seasons)
Using GitHub to Look at Source for a CVE [HackTheBox – Forgot]

191 – Param Pollution in Golang, OpenEMR, and CRLF Injection
Risky Biz News: White House unveils National Cybersecurity Strategy
Headless Browser SSRF & RebindMultiA Tool Release + Web3 Bug


Directory Traversal, File Include, File Upload — Web For Pentester 1
Bypass SSL Pinning on Flutter iOS App Using Frida and OpenVPN
Exploring Web3 Security: A Step-by-Step Guide to Creating Proof of Concepts for Previous Findings
Intro to Cloud Security | Tryhackme Writeup/Walkthrough | By Md Amiruddin
The Wild World of Website Tech: HTTP Requests, TCP Connections, and Bug Bounties — Oh My!
Exploring iOS Applications with Frida and Objection: Basic Commands for Pentesting

IDOR Vulnerability at /myaccount/myorders/getShipmentAndItemData lets attacker view other user’s…
What is the Open Redirect vulnerability, find it, and protect against it
My Report on How I avoid That XSS out of Scope when I discovered XSS and How can I convert it to…
30-Minute Heist: How I Bagged a $1500 Bounty in Just few Minutes!
How I was able to access 2 million user’s data in the web3 domain( Another critical bug in crypto
How I Earned $$$ for Excessive Data Exposure Through Directory Traversal Leads to Product Price
My Journey Finding HTML Injection Vulnerability in a popular British Accountancy platform
How an IDOR Can Wreak Havoc: Breaking through the front door!
Attacker Can Takeover Any Account Because of Misconfiguration of Invite Members (Bug-Bounty)
SSRF That Allowed Us to Access Whole Infra Web Services and Many More
How I Earned $1800 for finding a (Business Logic) Account Takeover Vulnerability?
My First Un-Expected $$$$ Digit Bounty for an Un-Expected Vulnerability


You may also like

August 28, 2026
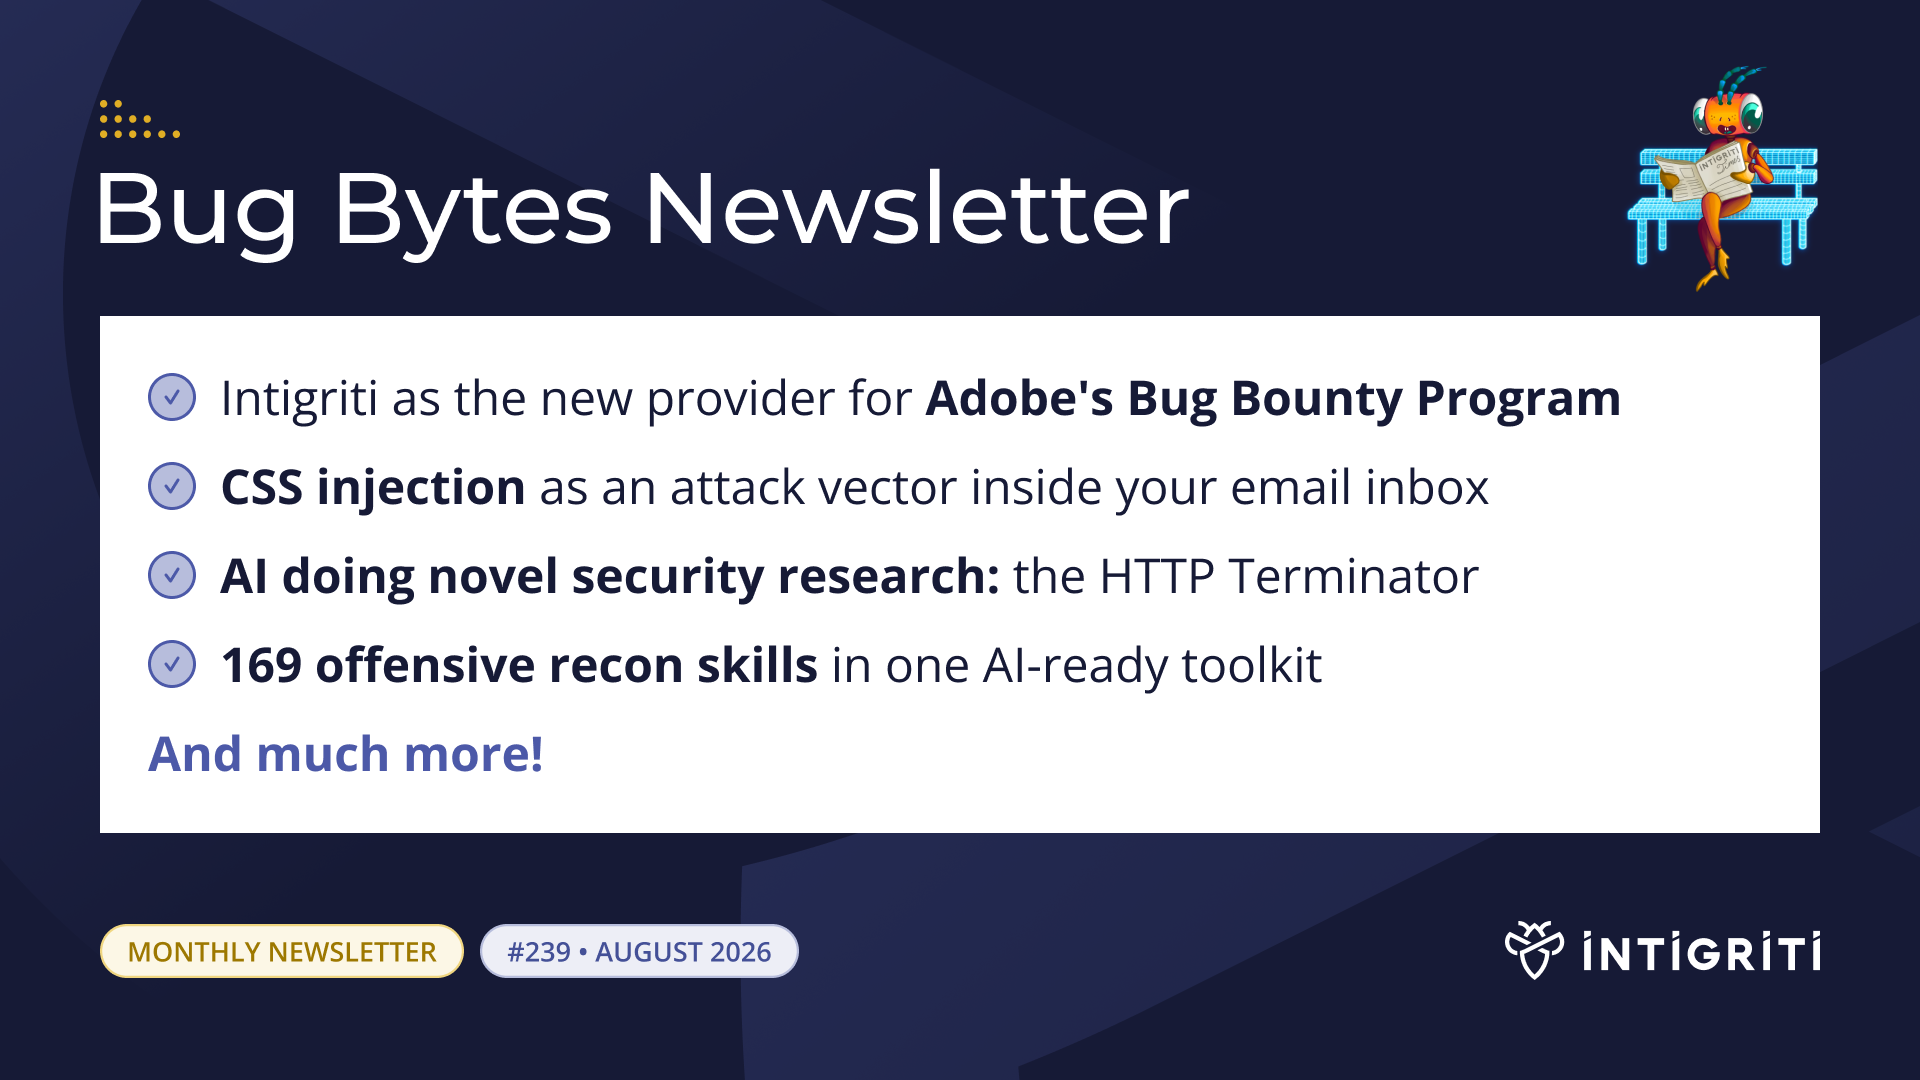
Intigriti Bug Bytes #239 - August 2026 🚀
Welcome to the latest edition of Bug Bytes! In this month's issue, we are featuring: Intigriti as the new provider for Adobe's Bug Bounty Program CSS injection as an attack vector inside your email inbox AI doing novel security research: the HTTP Terminator 169 offensive recon skills in one AI-ready
July 31, 2026
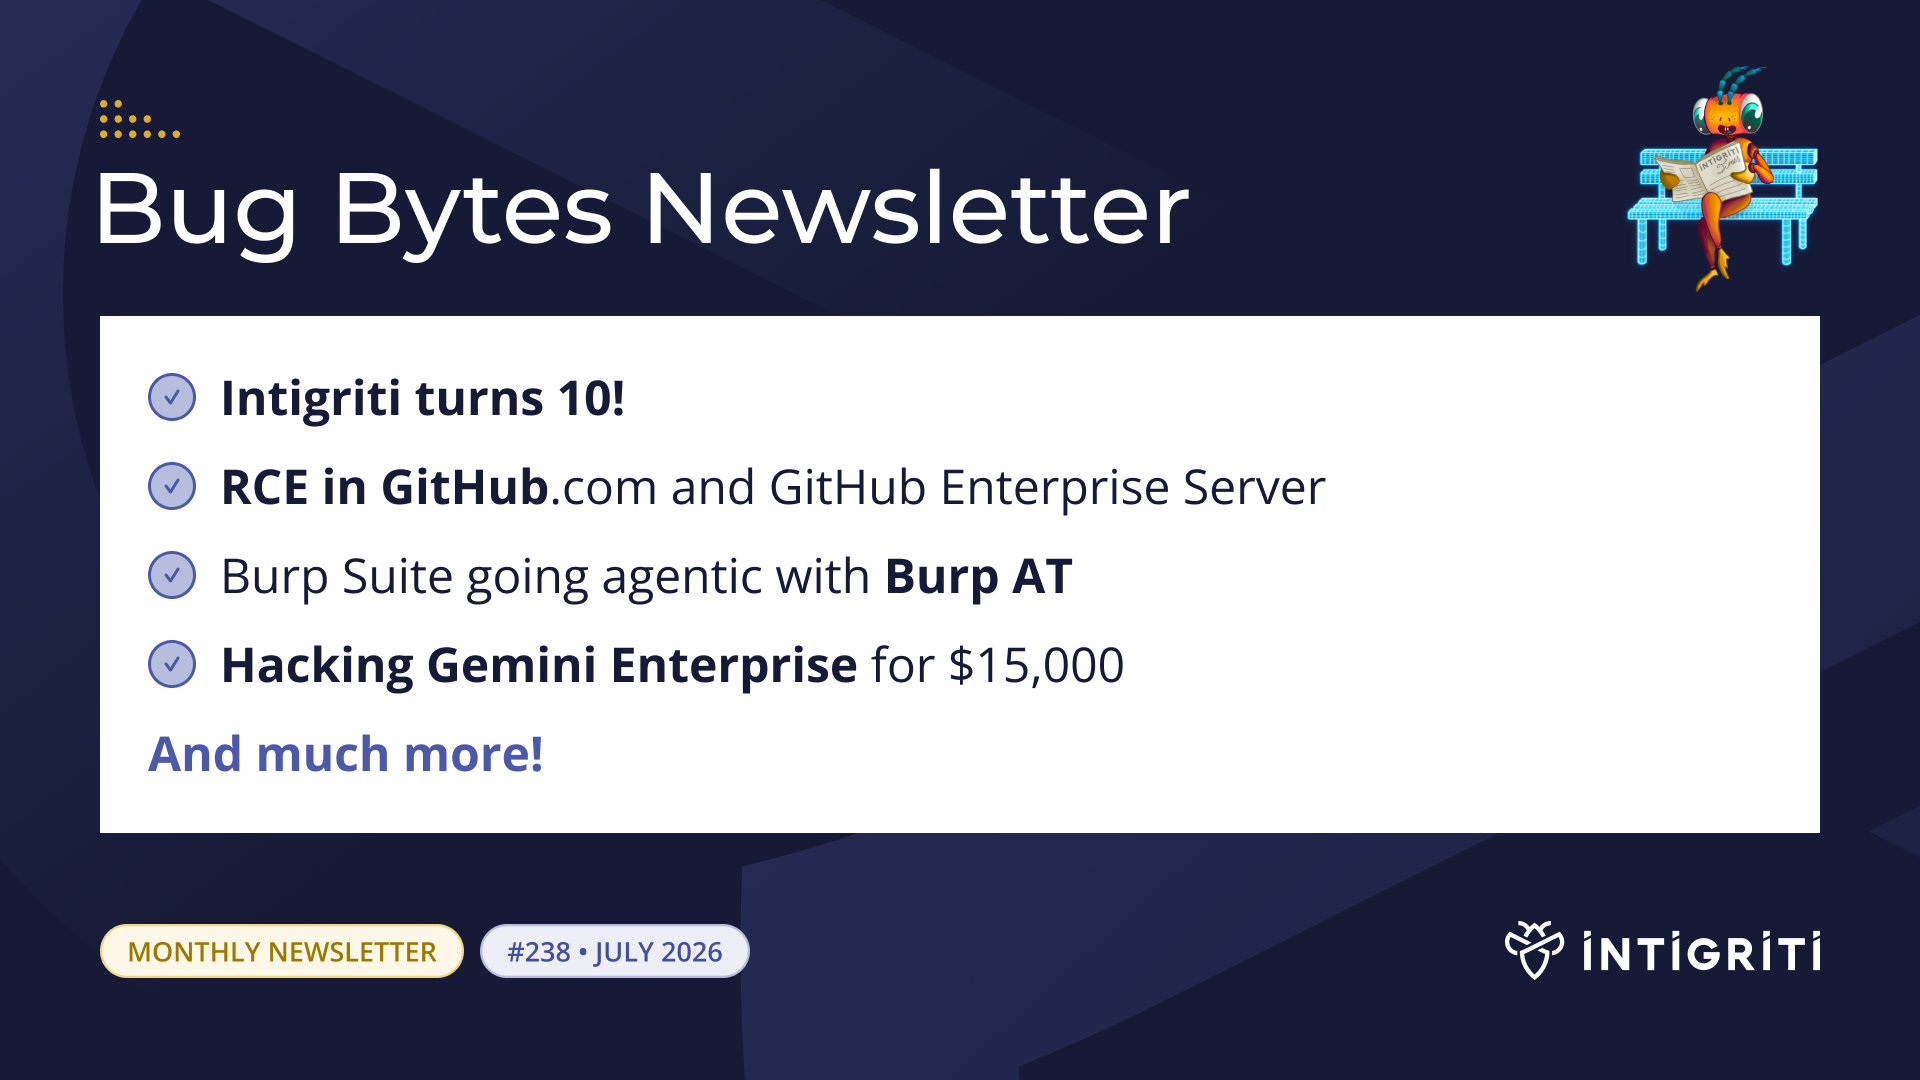
Intigriti Bug Bytes #238 - July 2026 🚀
Welcome to the latest edition of Bug Bytes! In this month's issue, we'll be featuring: Intigriti turns 10! RCE in GitHub.com and GitHub Enterprise Server Burp Suite going agentic with Burp AT Hacking Gemini Enterprise for $15,000 3,708 live credentials found by scanning GitHub Archive And so much mo
June 26, 2026
Intigriti Bug Bytes #237 - June 2026 🚀
Welcome to the latest edition of Bug Bytes! In this month's issue, we are featuring: A 10-year-old pre-auth RCE in phpBB Earning $500K hacking Google with AI Reading any Salesforce Marketing Cloud account's emails New DOMPurify sanitizer bypass Mapping abandoned S3 buckets to redo SolarWinds at scal