






Get more from your security testing program
Combining a global community of skilled researchers with deep program expertise and an enterprise-ready platform, we help strengthen your security as environments and business priorities evolve.
Intigriti helps security teams, like yours, continuously identify and validate vulnerabilities with real impact. By bringing the right researchers to each challenge and validating findings before they reach you, we provide a clear understanding of exposure and the confidence to focus efforts where they have the greatest effect.
Our clients include


Factors slowing down your team?

Your backlog was already full. AI increased code volume, release speed, and vulnerability submissions.

More findings do not always mean more vulnerabilities. Duplicates, unclear reproduction steps and low-context reports still need expert triage.

Proof of exploitability, not a list of potential vulnerabilities. Pay for impact, not time or tokens.

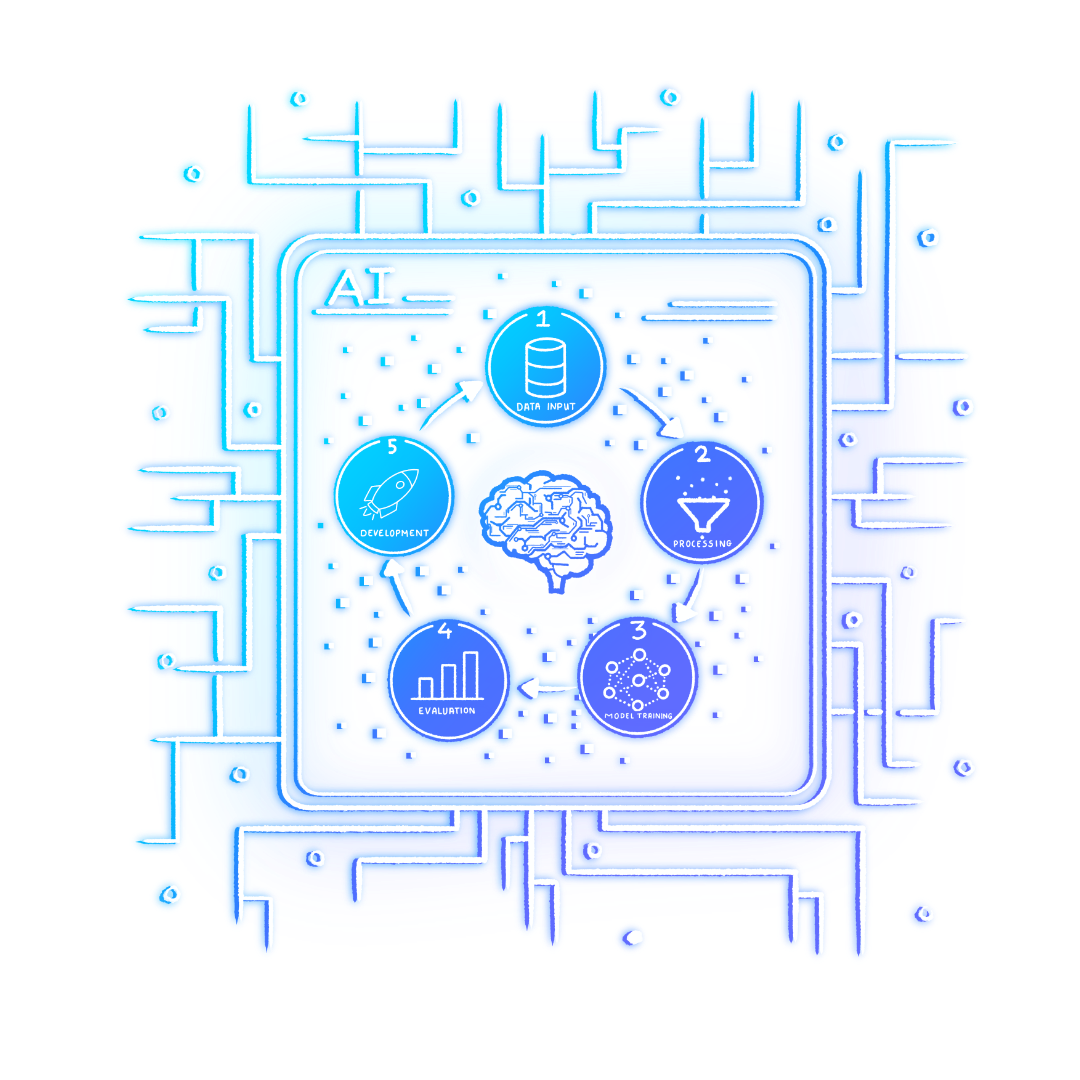
AI systems change fast, with model updates, prompt changes, new tools, and new retrieval sources. Continuous testing helps you keep pace as the risk surface evolves.
Our services
The right researchers for your environment, findings validated before they reach your team, program expertise focused on outcomes, not submission volume.
Start with Intigriti for a curated, contextual approach to continuous security testing, built around your attack surface, technology, and risk profile.

Bug bounty
Ethical hackers test your company’s web applications, enterprise infrastructure, and other digital assets for security vulnerabilities.

PTaaS
Launch tests in days, collaborate directly with expert researchers, and get real-time, actionable results, integrated into your security tools.

Intigriti VDP
The safe harbor researchers need, plus the expert analysis you want, enabling your team to act fast and focus on impact.

Live hacking events
Harness the power of our ethical hackers in a unique setting with maximum impact. Launch a live event to take your program to the next level.


Turn hacker reconnaissance into actionable insights
CrowdRecon helps security teams understand real researcher behavior across their attack surface, while giving researchers new ways to be recognized and rewarded beyond accepted vulnerability reports.
Switch without starting over
Want to migrate to Intigriti, but don’t want to lose your program history? Provide one API key, and our engineers will handle the export, mapping, and import with zero customer engineering effort.

Switching is simple
All you need to do is provide your API key, and we take care of everything else. Every report, conversation, decision, and attachment comes across with you.
An asset, not an archive
Once inside Intigriti, your data is fully structured and searchable, ensuring your past insights continue to power your decision-making.


View our latest blog!
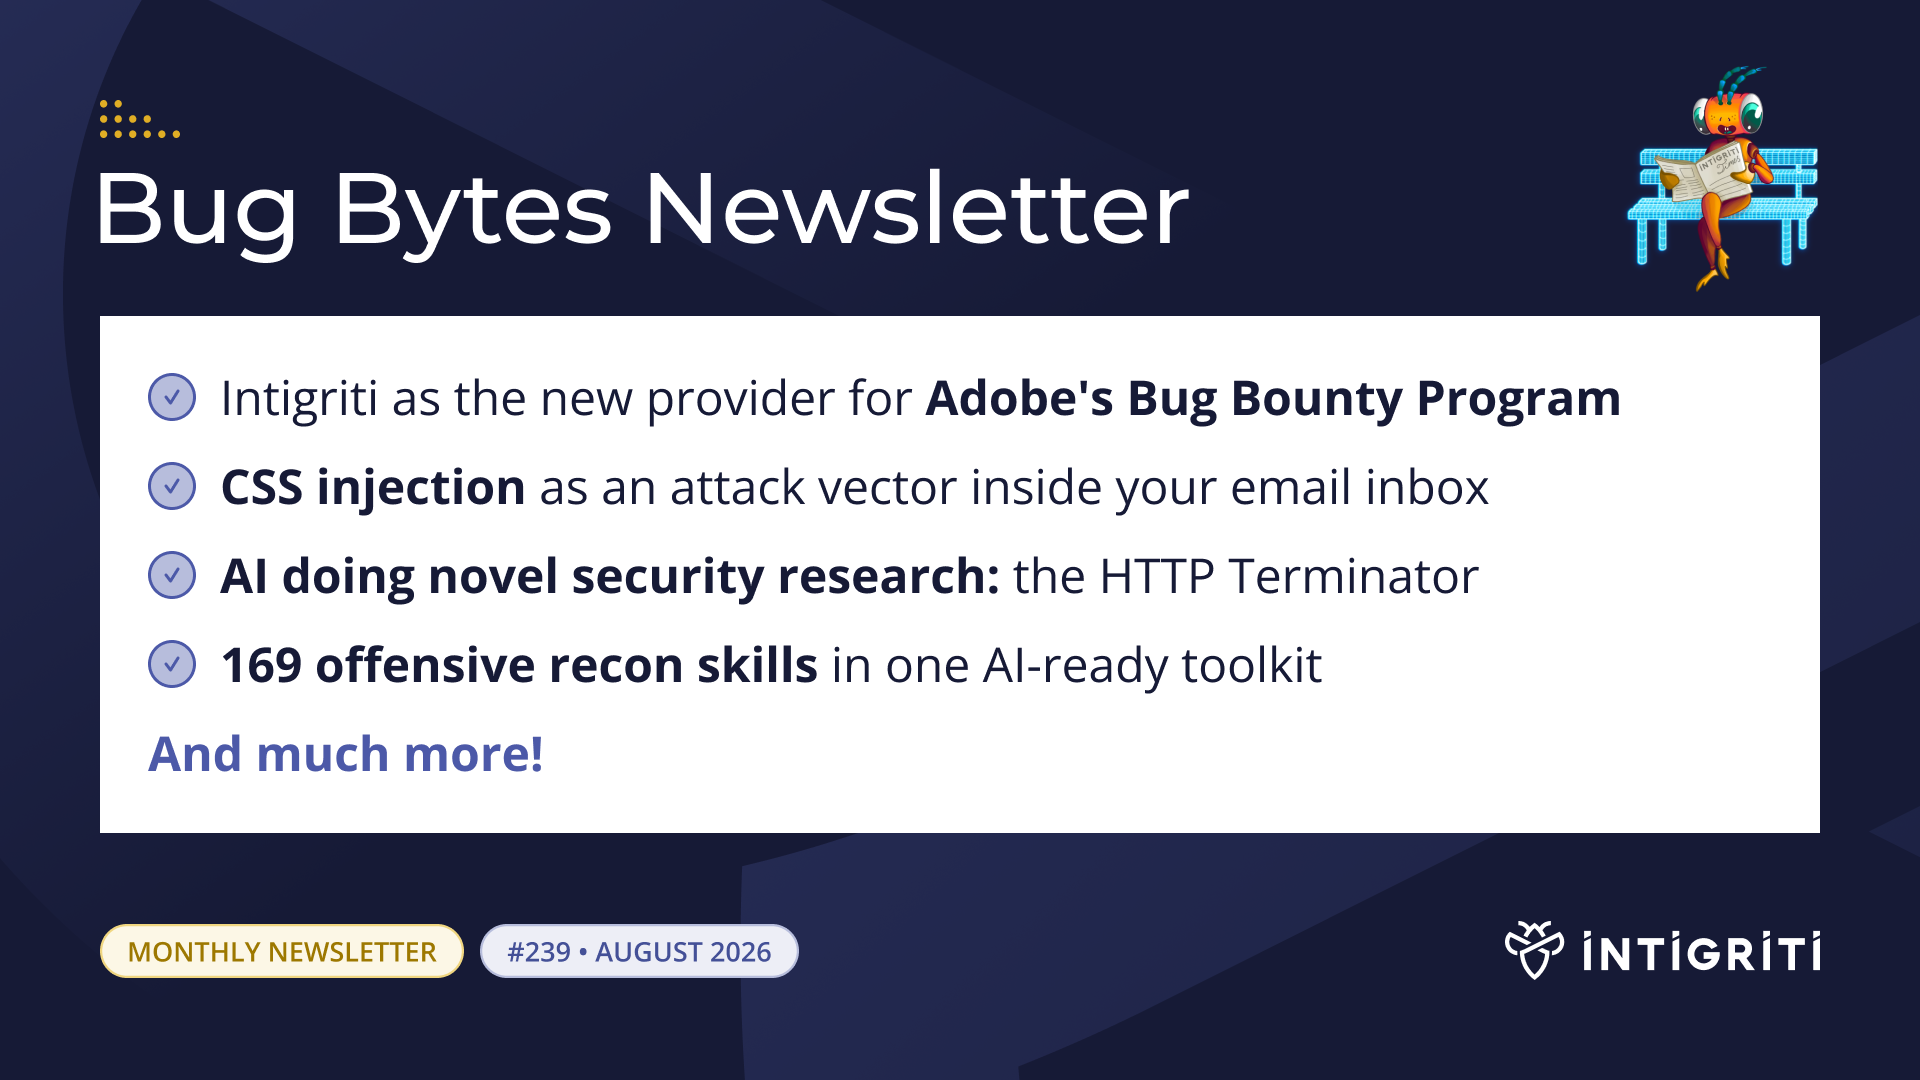
Adobe chose Intigriti as the new home of its Bug Bounty Program
"At Intigriti, we believe the strongest security comes from working alongside the hacking community. Our focus is on giving Adobe researchers an outstanding experience and supporting that community's continued growth. We are honored that they have chosen us as the new home for their Bug Bounty Program, and we see this as the start of a long and rewarding partnership."
Stijn Jans
CEO and Founder, Intigriti
World-class customer success
Intigriti’s customer success isn't a department; it's a commitment.
Dedicated support: Our customer success team is passionate about understanding your unique needs and providing tailored assistance to drive your success.
Expert guidance: Get insights, recommendations, and best practices to make informed decisions and achieve your cybersecurity goals.
Empowering your journey: From initial onboarding to ongoing consultations, we're committed to helping you optimize your security strategy.


Validated findings
Your team works on proof of exploitation, not on a list of potential vulnerabilities. Finding that reaches your team has been validated for:
Accuracy
Severity
Relevance

Operating standards that enterprises trust
European-built, globally trusted. GDPR by design, CVS Numbering Authority, SOC 2 Type 11, and ISO27001 certified.
Mandatory ID checks for bug bounty researchers: We conduct mandatory ID checks for all payments, adding an extra layer of verification to ensure the highest level of protection and compliance.
Application-level encryption: Your data's security is our top priority. We utilize application level encryption to guarantee that your sensitive information remains protected and confidential at all times.


Matched researchers
Every program is built with researchers matched to your specific attack surface, tech stack, and risk profile, selected for the skills and track record that fit with what your scope requires.
Fully vetted, ID-checked talent
Flexible team that scales with you
Backed by Intigriti's triage team
Request Pricing
Ready to see what Intigriti can do for you? Request a quote today!